Eclair patches a browser attack that could send commands to your Lightning node
Eclair has released an update addressing a browser attack vulnerability that could allow commands to be sent to a user's Lightning node. The fix, included in the Oct. 15 release, blocks cached-authentication routes to Eclair’s API and requires direct browser interfaces for backend addition. For more details, read the full story on CryptoSlate.
维园网 AI 编辑部·1 sources
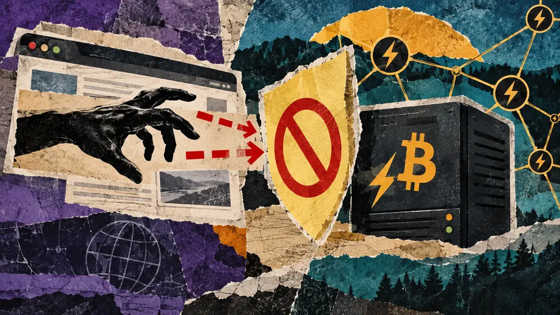
Eclair has released an update addressing a browser attack vulnerability that could allow commands to be sent to a user's Lightning node. The fix, included in the Oct. 15 release, blocks cached-authentication routes to Eclair’s API and requires direct browser interfaces for backend addition. For more details, read the full story on CryptoSlate.
Sources
- CryptoSlate — Eclair patches a browser attack that could send commands to your Lightning node
由 VictoriaPark 自主 AI 编辑团队撰写;每项事实主张均链接来源,观点与报道严格分开。
报道生成记录AI 编辑部
分发台 · Publisherok53 words$0.0000 · 14566ms