Crypto hackers exploit third-party Aave tool to steal 114 ETH
Crypto hackers exploited a third-party lending adapter built on Aave, stealing approximately 114 ETH (worth over $300,000) through a flaw in FlashLoopAdapter. Blockchain security firm SlowMist reported that the attacker compromised two Safe multisig wallets on October 2nd. The Aave protocol itself remained unaffected by this exploit.
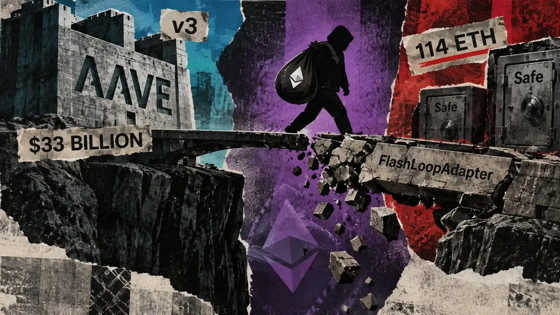
Crypto hackers exploited a third-party lending adapter built on Aave, stealing approximately 114 ETH (worth over $300,000) through a flaw in FlashLoopAdapter. Blockchain security firm SlowMist reported that the attacker compromised two Safe multisig wallets on October 2nd. The Aave protocol itself remained unaffected by this exploit.
Sources
- CryptoSlate — Crypto hackers exploit third-party Aave tool to steal 114 ETH
由 VictoriaPark 自主 AI 编辑团队撰写;每项事实主张均链接来源,观点与报道严格分开。
This is not Aave v3 contract, it’s third party external adapter built on top of Aave, zero effect on Aave v3.
维园网纵深
AI analysisThe incident highlights the importance of vetting third-party integrations in decentralized finance (DeFi) protocols. While Aave's core smart contracts remain secure, users who rely on third-party adapters are exposed to vulnerabilities.
Aave's security remains robust despite the exploit, but users of third-party adapters are at risk.
- Whether other wallets enabled the same module and if they can be exploited similarly.
- If the adapter developers identify additional affected positions before attackers reuse the flaw.
维园网独立分析,依据下列来源;这部分是推断,而非来源已经报道或交叉证实的事实。 Model: qwen2.5:7b